The European Union has established a rigorous regulatory framework through the Markets in Crypto-Assets (MiCA) regulation to manage the risks associated with digital asset service providers. This regulatory push coincides with a period where Decentralized Finance (DeFi) has moved from a niche experimental sector to a primary pillar of the global digital economy. As this transition accelerates, the DeFi wallet has emerged as the essential interface for interacting with decentralized protocols, functioning as more than just a storage solution but as a comprehensive cryptographic identity. Unlike traditional financial systems that rely on trusted intermediaries to safeguard assets and verify identities, the decentralized model places the burden of security and operational integrity directly on the individual. This shift necessitates a deep understanding of the technical mechanics and legal nuances that define the modern financial landscape, especially within the context of evolving standards that aim to protect consumers without stifling the permissionless nature of blockchain technology.
The Foundations: Self-Custody and Digital Sovereignty
At its fundamental level, a DeFi wallet operates as a sophisticated key management system rather than a container that physically holds digital currency. In the traditional banking sector, an institution holds funds and provides access via passwords or biometric checks, but in the blockchain environment, assets exist exclusively as ledger entries on a distributed network. The wallet serves as a repository for the private key, a complex numerical string that allows a user to sign and authorize transactions that move these ledger entries. This concept of self-custody is the cornerstone of financial sovereignty, as it ensures that no government, bank, or corporation can freeze an account or prevent a valid transaction from occurring. However, this absolute control is a double-edged sword; because the wallet simply manages keys, the responsibility for keeping those keys secure is absolute. There is no central authority to reset a lost recovery phrase, meaning that the user is the sole guardian of their financial future in a way that was previously impossible in the conventional financial world.
The distinction between using a DeFi wallet and a centralized exchange (CEX) highlights a significant trade-off between institutional safety nets and individual freedom. Centralized platforms like Bitpanda or Coinbase are regulated entities that hold the user’s keys and are subject to stringent licensing requirements under the MiCA regulation, providing features such as customer support, fraud monitoring, and even insurance in some cases. These platforms manage the complexity of blockchain interactions behind a user-friendly interface, making them ideal for beginners or those who prefer a traditional service model. In contrast, DeFi wallets provide an unfiltered gateway to the entire decentralized ecosystem, allowing users to engage in peer-to-peer lending, liquidity provision, and governance voting without seeking permission from an intermediary. This direct access removes the counterparty risk associated with centralized exchanges—which can face insolvency or technical failures—but it introduces a high level of operational risk, where a single mistake in transaction signing can lead to the permanent and irreversible loss of capital.
Architecture: Comparing Wallet Types and Security Profiles
The technological categorization of DeFi wallets reflects a continuous struggle to balance ease of use with the need for robust security. Hot wallets, which include browser extensions and mobile applications, are the most common tools for daily interaction with decentralized applications because they are always connected to the internet. Browser-based wallets like MetaMask or Phantom allow for seamless integration with desktop trading platforms, but they remain inherently vulnerable to malware, such as keyloggers or malicious scripts, that can compromise the host device’s memory. Mobile applications offer a slightly more secure alternative by utilizing the isolated “sandboxing” environments found in modern smartphone operating systems, which prevent different apps from accessing each other’s sensitive data. These mobile interfaces frequently use protocols like WalletConnect to bridge the gap between a handheld device and a desktop web interface, providing a layer of separation that can mitigate some of the risks associated with standard browser-based interactions.
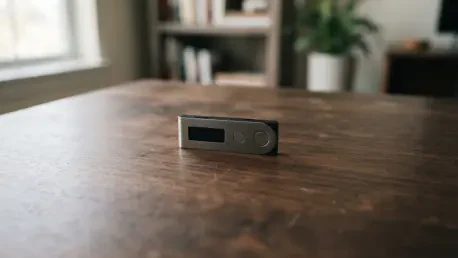
Hardware wallets, often referred to as cold storage, represent the highest standard of security for anyone serious about protecting their digital assets. These physical devices are designed to generate and store private keys in an offline environment, ensuring that the sensitive cryptographic data never touches an internet-connected computer or phone. When a user wishes to make a transaction, the hardware wallet signs the message internally and only sends the resulting signature back to the connected device, meaning that even a computer infected with the most sophisticated viruses cannot steal the keys. The security of these devices is bolstered by the requirement for physical confirmation; a user must manually press a button on the hardware to authorize any outgoing movement of funds. While this adds a layer of friction to the user experience, it creates a physical barrier that remote attackers cannot overcome. Nevertheless, even a hardware wallet is not a panacea for poor judgment, as it will faithfully execute any malicious transaction or signature request that a user chooses to confirm, emphasizing the ongoing need for user vigilance.
Vulnerabilities: The Mechanics of Malicious Permissions
Successful interaction with the decentralized ecosystem requires a nuanced understanding of the different ways a wallet communicates with a smart contract. The process typically begins with a “connection” request, where a dApp asks to view the user’s public address and token balances. This action is generally low-risk because it does not grant the application permission to move any funds. The danger begins with the “signing” and “transacting” phases, which are the primary targets for malicious actors. Transactions are on-chain actions that require the payment of a gas fee and result in an immediate change to the state of the blockchain, such as swapping one token for another. In contrast, digital signatures are often performed off-chain and do not cost any fees, which often leads users to believe they are safer. However, modern cryptographic standards allow these signatures to function as a digital power of attorney, enabling an attacker to gather a signature and then broadcast it later to drain the user’s account without any further interaction from the victim.
Token approvals, or allowances, are perhaps the most misunderstood and exploited technical feature in the current DeFi landscape. When a user interacts with a decentralized exchange or a lending protocol, they must first “approve” the protocol’s smart contract to spend a specific amount of their tokens. To save users from the inconvenience and cost of paying for multiple approval transactions, many applications request an “unlimited” allowance by default. While this is convenient for high-frequency traders, it essentially leaves a “spare key” to the wallet in the hands of the smart contract. If that contract is ever exploited by a hacker—even years after the user last visited the site—the attacker can use those existing permissions to withdraw all the approved tokens directly from the user’s wallet. This vulnerability has led to numerous high-profile drainer attacks where individuals lost millions of dollars because they failed to manage their open allowances, proving that security in DeFi is not just about the initial setup but about the long-term management of digital permissions.
Sophisticated Attacks: Phishing and Protocol Exploitation
The security landscape in 2025 indicated that while overall awareness is increasing, the methods used by scammers have become significantly more surgical and difficult to detect. Signature phishing has emerged as a primary threat, specifically targeting “Permit” signatures that allow for token transfers without an initial approval transaction. These attacks are particularly effective because the signature requests often look identical to benign login prompts or harmless message verifications. One high-value victim in early 2025 lost over $6.5 million in a single instance after unknowingly signing a Permit message on a spoofed website. These “wallet drainer” scripts are now sold as professional services on the dark web, complete with customer support and frequent updates to bypass the latest security features implemented by popular wallet providers. This industrialization of cybercrime means that every user, regardless of the size of their portfolio, is a potential target for automated scripts designed to identify and exploit any weakness in their signing habits.
Technological advancements intended to improve the blockchain experience have also been repurposed by attackers to facilitate more complex thefts. The implementation of EIP-7702, which was part of a major network upgrade in May 2025, introduced the ability for standard addresses to temporarily take on the characteristics of smart contracts. While this was designed to enable features like transaction bundling and social recovery, scammers quickly realized they could use it to trick users into signing delegation messages. Once a user signs such a message, the attacker can effectively “upgrade” the victim’s address to a contract under the attacker’s control, granting them the ability to perform complex operations and bypass traditional security checks. This constant cat-and-mouse game between developers and malicious actors underscores the reality that in DeFi, innovation and risk are inextricably linked. Each new feature that adds flexibility to the user experience also creates a new potential attack vector that requires a corresponding evolution in security practices and user education.
Operational Challenges: Gas Management and Network Interoperability
Beyond the immediate concerns of cybersecurity, users of DeFi wallets must navigate the operational complexities of managing funds across a fragmented landscape of different blockchains and scaling solutions. Every action taken on a blockchain requires the payment of a “gas fee” in the network’s native token, such as Ether for Ethereum or SOL for Solana. A frequent and frustrating error for beginners involves holding a significant amount of stablecoins or other tokens on a specific network but failing to keep a small amount of the native token to pay for transaction costs. This results in funds being effectively “stuck” until the user can acquire the necessary fuel from an external source. As the industry has shifted toward Layer-2 scaling solutions like Arbitrum, Optimism, and Base to reduce costs, the problem of gas management has become even more acute, requiring users to maintain a complex inventory of various native tokens across multiple independent environments to remain operational.
The rise of these Layer-2 networks has also introduced significant risks regarding address management and network interoperability. Because many of these networks use the same address format as the Ethereum mainnet, a user’s address will look identical across dozens of different chains, leading to the mistaken belief that assets are automatically accessible everywhere. This is not the case; tokens sent to a regulated exchange or another wallet via the wrong network can be permanently lost if the receiving party does not support that specific chain. Furthermore, the bridges used to move assets between these networks are themselves frequent targets for hacks and technical failures. Users must exercise extreme caution when performing cross-chain transfers, verifying that both the sending and receiving interfaces are configured for the correct network. This level of technical oversight is a far cry from the “send and forget” simplicity of traditional wire transfers, requiring a disciplined approach to every movement of capital within the decentralized ecosystem.
Compliance: Navigating the European Regulatory Environment
The European Union has taken a decisive lead in bringing order to the digital asset space through the full implementation of MiCA and the Transfer of Funds Regulation (TFR). These rules are primarily designed to regulate the behavior of Crypto-Asset Service Providers (CASPs) rather than the individual developers who write open-source code for self-custody wallets. However, the impact on the end user is profound, particularly when moving assets between the regulated world of exchanges and the permissionless world of DeFi. Under the TFR, which became fully applicable at the end of 2024, any transfer from a regulated exchange to a self-custody (unhosted) wallet that exceeds a value of €1,000 triggers a mandatory verification process. The exchange is required to confirm that the customer actually owns or controls the destination wallet, a process that has introduced new technical hurdles for users who previously enjoyed the anonymity of decentralized addresses.
This verification requirement typically involves the user performing a “Satoshi test,” which is a small, specific transfer of funds, or signing a unique cryptographic message to prove they possess the private keys to the address. These measures are part of a broader European effort to combat money laundering and the financing of terrorism by ensuring that every large transaction has a documented origin and destination. While some privacy advocates have criticized these rules as overreaching, they have also provided a level of legitimacy to the industry that has encouraged institutional participation. For the individual user, this means that maintaining a clear and transparent audit trail of all on-chain activities is no longer optional. When it comes time to move profits back into a regulated bank account, exchanges will often demand a full history of where the funds originated. Users who fail to keep accurate records or who interact with high-risk protocols may find their accounts frozen or their transactions rejected by compliant service providers.
Proactive Security: Strategic Hygiene for Long-Term Safety
The evolution of the decentralized landscape demonstrated that maintaining financial security was not a singular event but a continuous process of digital hygiene. Successful participants in the ecosystem realized that the most effective defense against theft was the limitation of the “blast radius” for any potential exploit. This was achieved by moving away from the dangerous habit of granting unlimited token approvals and instead manually entering the exact amount of currency required for each specific transaction. Furthermore, the routine use of specialized tools to audit and revoke outstanding permissions became a standard practice for protecting long-term holdings. By identifying and closing old backdoors to their wallets, users were able to effectively secure their assets against vulnerabilities in protocols they had not used in months or even years. This proactive approach to permission management proved to be the single most effective way to mitigate the risk of automated wallet drainers.
Actionable steps were identified as essential for long-term safety, including the strict separation of digital identities through the use of multiple wallet addresses. Individuals were encouraged to maintain a “vault” address, which held the majority of their long-term savings and never interacted with new or unverified smart contracts, while utilizing a separate “burner” address for experimental or high-frequency activities. This compartmentalization ensured that even if a user was tricked by a sophisticated phishing attack on a new dApp, the majority of their wealth remained isolated and secure. The industry also saw a shift toward the integration of transaction simulations, which provided users with a clear preview of exactly what tokens would leave their account before they authorized a signature. As the digital asset space continues to mature throughout 2026 and into 2028, the transition from a passive consumer mindset to an active, informed participant will remain the only reliable way to enjoy the benefits of financial sovereignty while minimizing the inherent risks of the decentralized frontier.