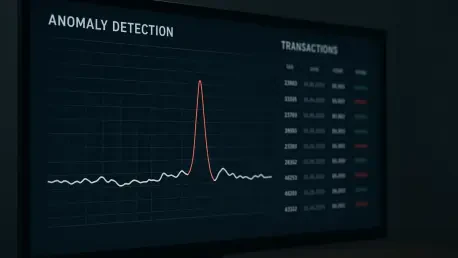
The quiet preparation phase of a sophisticated operation involves performing benign activities that neutralize the effectiveness of standard anomaly detection software. In the current landscape of 2026, the traditional boundaries of financial security have dissolved as generative artificial intelligence has fundamentally altered how illicit actors interact with banking infrastructure. For years, the industry relied on the assumption that criminal behavior is inherently erratic, characterized by sudden spikes in transaction volume or logins from geographic outliers. However, the emergence of highly sophisticated AI models has allowed fraudsters to automate legitimacy, creating digital footprints that are indistinguishable from those of high-value, law-abiding customers. This shift from brute-force exploitation to subtle mimicry has created a tipping point where identifying a single suspicious event is no longer sufficient to protect assets. Institutions must pivot toward a model rooted in contextual intelligence that looks beyond isolated logs to understand the broader narrative of an entity.
The Limitation: Why Outlier Detection Fails in the AI Era
Modern fraudsters no longer rely on obvious red flags that trigger automated alerts; instead, they have mastered the art of blending into the digital crowd. By utilizing sophisticated machine learning tools to automate the creation of “normal” behavior patterns, these criminals can maintain accounts that appear perfectly healthy for extended durations. These accounts perform low-value, benign transactions that satisfy the strict criteria of traditional detection models, effectively neutralizing the safety nets that once protected global finance. The fundamental challenge lies in the fact that a transaction can be perfectly normal from a statistical standpoint while being entirely fraudulent in its ultimate intent. When an account is meticulously aged and its daily behavior is curated to mirror the habits of a model consumer, there is simply no anomaly for a standard system to detect. This development necessitates a complete change in the primary investigative question posed by risk management teams.
The limitation of legacy systems is most apparent when considering how AI-driven agents can now simulate the biological and digital inconsistencies of real humans. In previous years, automation was easy to spot because of its robotic precision, but current generative models introduce intentional variability that bypasses velocity checks and behavioral biometrics. Consequently, fraud teams must stop asking whether a specific transaction looks strange and start questioning whether the entire identity behind the transaction is grounded in physical reality. Relying on deviation from the norm assumes that a norm exists, yet AI can now manufacture custom “norms” for every fraudulent account it manages. This creates a state of perpetual plausible deniability for the attacker, who operates within the safe zones of pre-defined risk thresholds. Without a deeper understanding of the context surrounding the entity, financial institutions remain blind to the structural rot beginning to fester within their own user bases.
Identity Deception: The Rise of Synthetic Architecture
Synthetic identity fraud represents one of the most difficult challenges for modern risk teams because it combines legitimate data with fabricated, AI-generated assets to create a convincing whole. By pairing a real Social Security number with deepfake imagery and synthetic voice profiles, fraudsters create what are often called “Frankenstein” identities that pass automated verification checks with ease. These identities are not stolen in the traditional sense where a victim reports a lost card; they are manufactured from the ground up to exist within the technical gaps of current credit and banking systems. The danger of these synthetic entities lies in their ability to fool biometric systems that were once thought to be foolproof. With the advent of real-time video and audio synthesis, the cost of generating a unique, high-fidelity persona has dropped significantly, allowing criminal syndicates to flood the market with thousands of distinct identities that possess no real human counterpart.
These synthetic entities often undergo a lengthy period of incubation where they build credit and establish a history of reliable behavior through automated micro-transactions. During this phase, the account appears exceptionally low-risk to any automated system focused on historical consistency or debt-to-income ratios. It is only by looking at the broader context, such as the validity of the supporting documentation and the lack of an actual real-world footprint, that investigators can distinguish a loyal customer from a sophisticated criminal operation. The data itself can tell two diametrically opposed stories depending on the lens used for analysis. A system focused only on transaction logs sees a perfect customer, while an investigative approach focused on identity intelligence sees a void where a human history should be. This period of “quiet prep” is the new frontline of financial crime, where victory is won or lost before a single illicit transfer is even attempted by the fraudulent actor.
Structural Defense: Leveraging Graph Topology and OSINT
To counter criminals who hide behind “normal” behavior, institutions are turning to graph analytics to visualize the relationship topology of their entire digital networks. While traditional monitoring looks at accounts in isolation, graph models reveal the hidden structural connections between seemingly unrelated users across the globe. This allows investigators to see if dozens of apparently legitimate accounts are actually sharing the same hardware signatures, digital fingerprints, or ultimate beneficial owners. By shifting the focus from individual events to the complex connections between entities, organizations can identify entire fraud rings before they move into the active exploitation phase. Fraud is rarely an isolated incident in 2026; it is a structural problem involving vast networks of coordinated actors who use decentralized infrastructure to mask their footprints. Mapping these hidden patterns provides a proactive layer of security that catches blending strategies by exposing infrastructure.
Open Source Intelligence, or OSINT, serves as a vital bridge between internal digital data and real-world truth, allowing risk teams to validate the claims made by any given entity. For instance, while an account’s internal activity may look perfectly fine to an automated monitor, OSINT tools might reveal that the business’s website was created only yesterday or that its listed corporate address is actually a vacant lot in a different jurisdiction. This external layer of verification provides the strong circumstantial case needed to justify deeper human intervention and manual review. In an era where AI can manufacture internal legitimacy at scale, the only way to verify the truth is to cross-reference it against the vast, messy, and uncoordinated data of the physical world. Using automated web crawlers and public record databases, institutions can now verify the existence of real-world footprints, such as professional licenses and physical office locations, to ensure an entity is real.
Strategic Outcomes: Establishing Contextual Resilience
Ultimately, the most resilient defense systems utilize a Human-in-the-Loop model that pairs the processing speed of machines with the essential nuance of human judgment. While AI is excellent at processing massive datasets and spotting faint statistical correlations that humans might miss, people remain essential for interpreting intent and navigating the structural ambiguities of complex fraud cases. A unified engine that combines machine learning, graph analytics, and human intelligence represents the only viable path forward in an era of AI-generated deception. Human investigators can recognize the subtle “wrongness” of a situation that a model might overlook because it technically fits within the parameters of the training data. This synergy allows the machine to handle the heavy lifting of data aggregation and correlation while the human expert focuses on high-stakes decision-making and the investigation of edge cases. This collaborative approach ensures that the system evolves as quickly as the threats.
The shift toward contextual intelligence represented a fundamental change in how the industry approached risk and security during the current year. Financial institutions successfully moved away from reactive anomaly detection and instead implemented a unified defense layer that prioritized relationship mapping and external validation. This transition allowed security teams to dismantle several large-scale synthetic identity rings before they reached their intended “cash-out” phase, saving billions in potential losses. Organizations recognized that the battle against AI-driven fraud required a focus on the structural integrity of the entire user ecosystem rather than the scrutiny of isolated payments. By integrating OSINT and graph analytics into their core workflows, these institutions established a new standard for identity verification that emphasized the narrative over the event. The most effective leaders in the sector prioritized the development of adaptive systems that could distinguish between human inconsistency and calculations.